Site network security, under control
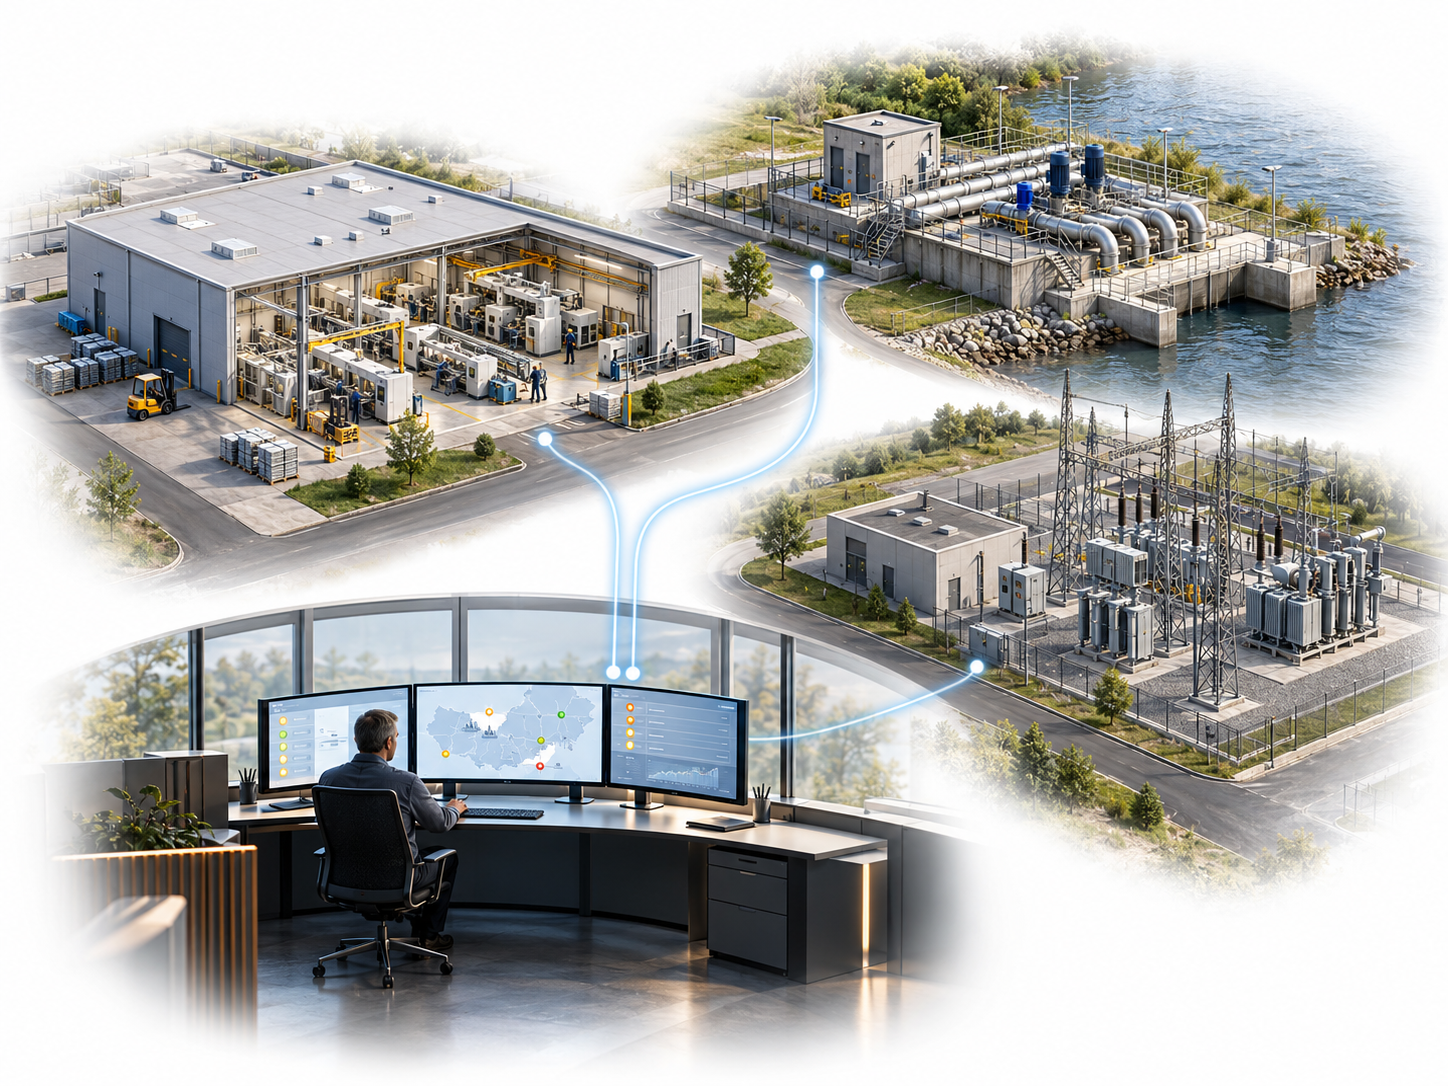
Routers at remote sites provide operational connectivity, administrative access and central visibility. Intelliport industrial routers, the M2M Platform and engineering services work together to protect these critical network points and support traceable operations and recovery.
The solution supports the site communications and device management layer of your organisation’s NIS2 risk management. We align controls with your risk assessment, security policies and incident management procedures.
Routers, the M2M Platform and expert services
Protection starts at the device, becomes traceable through central management and is sustained through controlled operations.
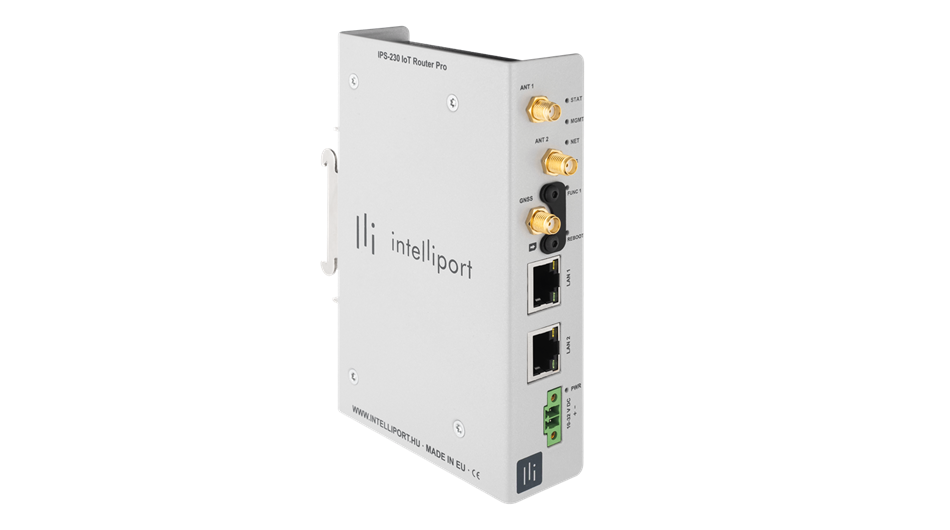
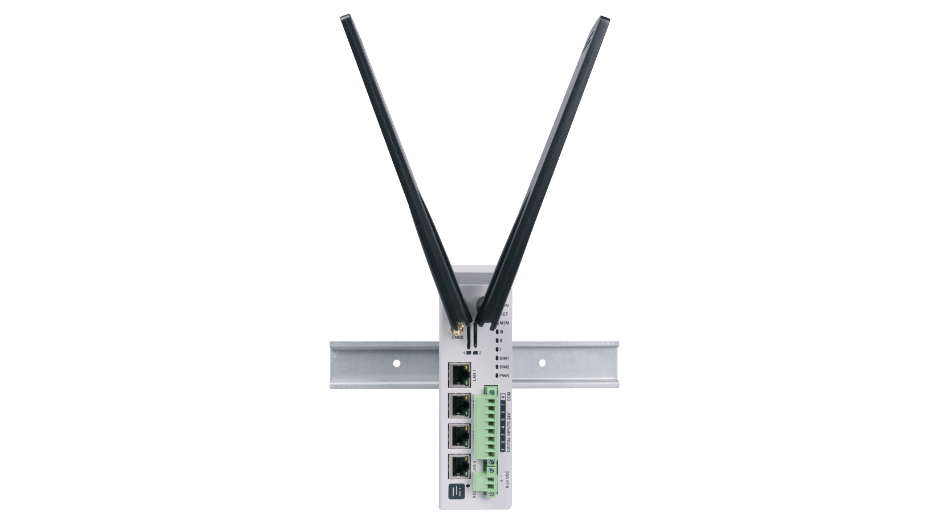
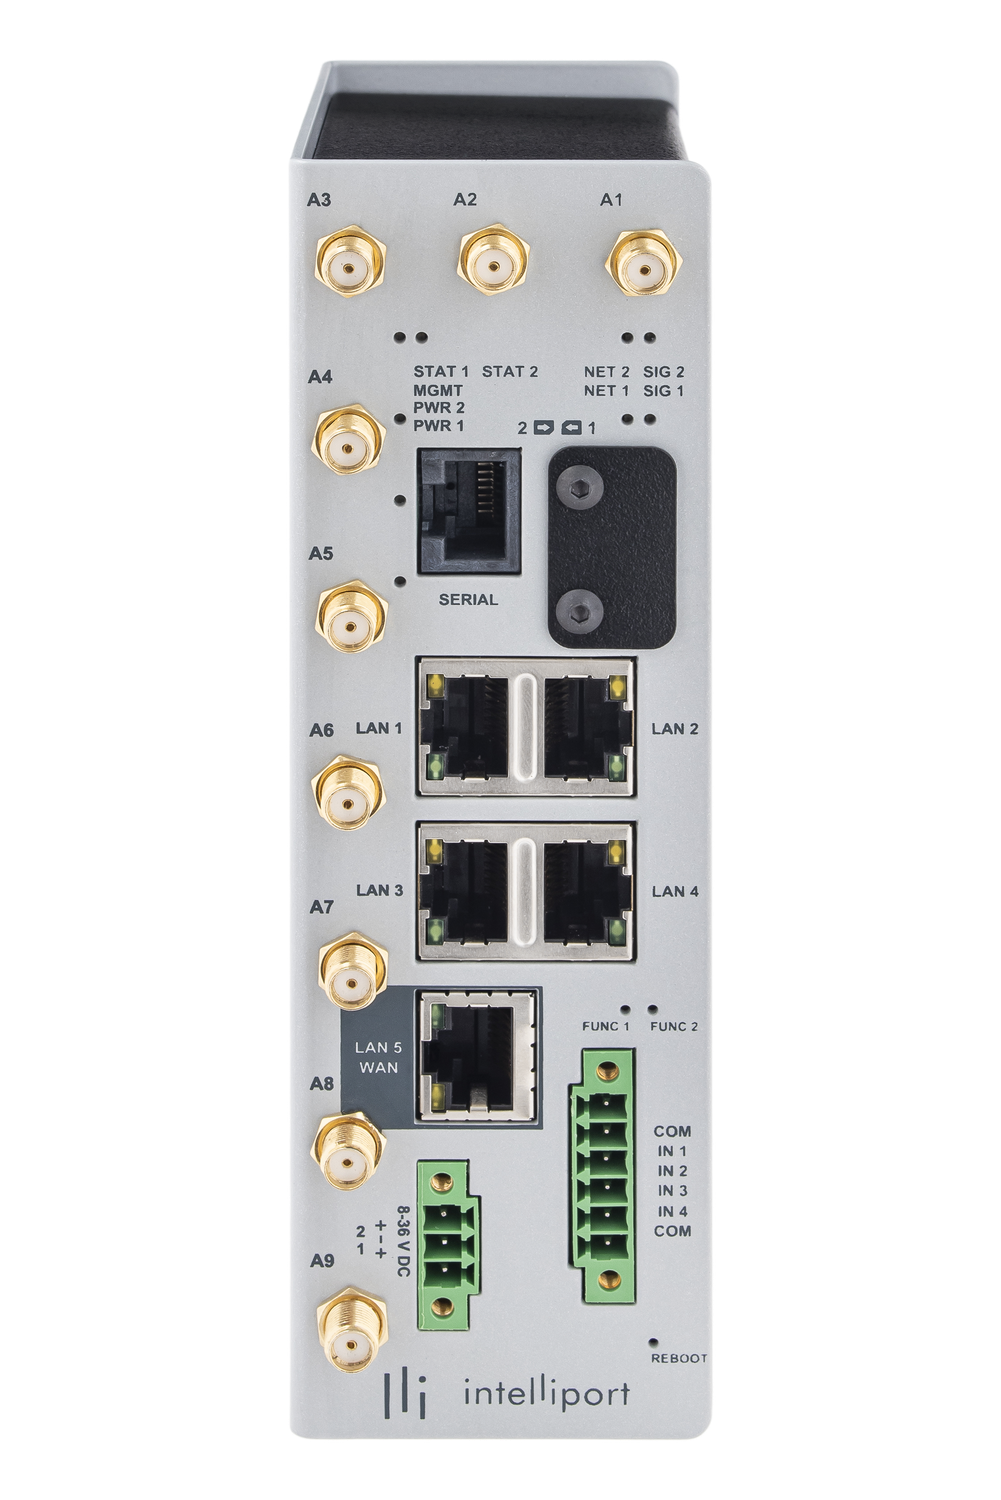
Industrial routers
Encrypted connectivity, network zones and firewall rules, remote management and availability features. We select the router and variant according to the required interfaces, security capabilities and redundancy.
Intelliport M2M Platform
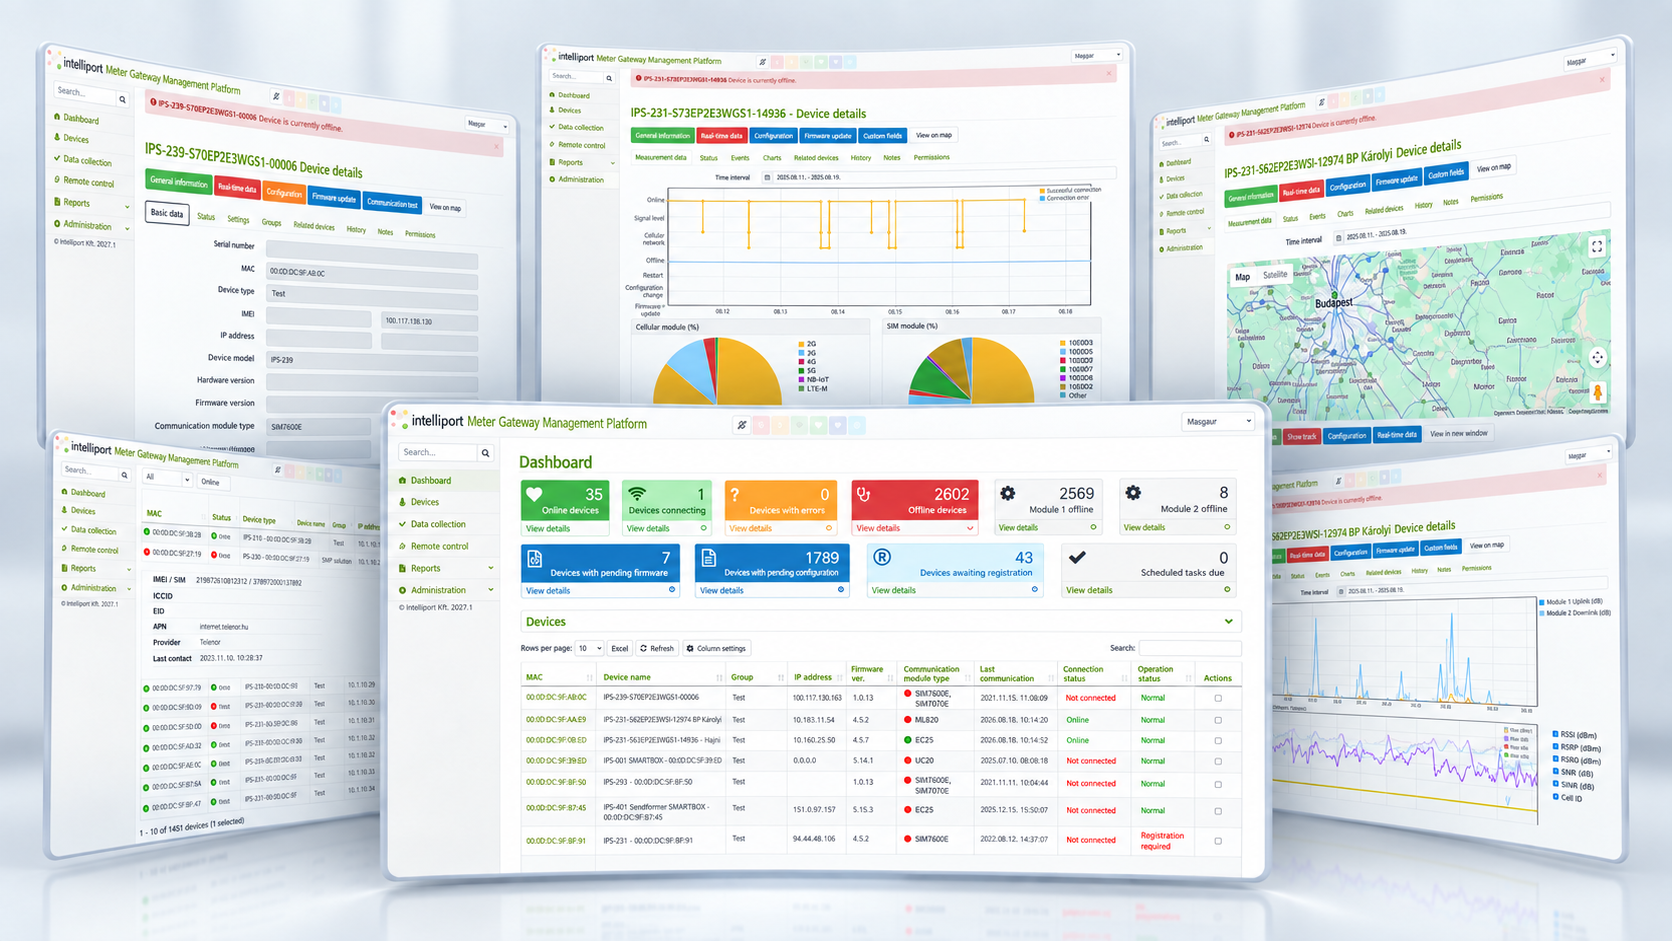
Central fleet overview, device status, role-based access, approval-controlled configuration and firmware changes, and logging of user actions.
Engineering delivery
Assessment, target architecture, security baseline, integration, pilot and site deployment. Responsibilities are defined across your IT team, systems integrator and Intelliport.
Ongoing support
Manufacturer expert support, agreed security update campaigns, configuration reviews, and lifecycle and availability monitoring.
Controls in everyday operations
We connect technical capabilities to operating procedures and retrievable evidence.
Asset inventory and visibility
An inventory organised by site and device group, with status and version data. Central visibility helps identify affected devices and prioritise replacements.
Controlled remote access
Encrypted management, roles and group-level administrative separation. MFA and identity management are designed around the selected devices, access infrastructure and your policies.
Logging and incident response
Router event logs and user actions recorded by the platform. Log export integrated with central collection or a SIEM, together with alert rules, supports event retrieval and incident investigation.
Configuration and updates
Approved baseline configurations, configuration comparison, and individual or group firmware and configuration updates. Deployment includes maintenance windows, a recovery plan and verification of results.
Segmentation and encryption
Designing separation between OT/IoT, operational and office traffic. VLANs, firewall rules and VPN connections are configured to match the selected router and network architecture.
Lifecycle and supplier support
Tracking firmware and support status, assessing vulnerability exposure, and defining replacement and recovery procedures. Manufacturer support records and intervention documentation also support audit preparation.
Backup connectivity for critical sites
The failure of a single wired link can interrupt both remote monitoring and intervention. A secondary mobile path and automatic switching form part of site business continuity.
- A mobile backup path alongside the primary wired connection, aligned with local coverage.
- Failover and failback policies, with multi-SIM or multi-modem arrangements according to the selected router.
- Planning a separate administrative access path during outages together with your network team.
- Switching and recovery tests covering reachability, VPN recovery and monitoring operation.
From assessment to sustainable operations
Delivery begins with an assessment of your existing environment and critical sites. Handover includes operational verification and agreed operating procedures.
Assessment and design
Review devices, site types, access paths and dependencies; define the target architecture, controls and responsibilities.
Hardening and integration
Configure baselines, permissions, encrypted access and logging; integrate with monitoring, identity and incident management systems.
Pilot and deployment
Reference-site trials, fleet rollout planning, switching tests and recovery procedures, followed by documented handover.
Operations and review
Updates, configuration and access reviews, lifecycle tracking and regular status reporting within the agreed service scope.
Traceable operations and prepared evidence
Audit preparation requires records of actions and tests alongside technical settings. The project defines the required data, retention procedures and handover documents.
- Device and firmware inventory with site and responsibility assignments.
- Approved configurations, change records and user action logs.
- Update campaign results and documented corrective actions.
- Switching and recovery test records, support and lifecycle information.